Iran's Silent War on U.S. Infrastructure — And Why the Pacific Should
The US confirms Iran has been targeting its critical infrastructure with cyberattacks since February. But recent high-profile outages at Microsoft and JP Morgan may not be linked. What does this mean for allies across the Pacific?
The admission most Americans won’t see in bold headlines
The United States government confirmed something quietly devastating on November 18: Iran has been conducting sustained cyberattacks against American critical infrastructure since a regional war erupted in February 2026.
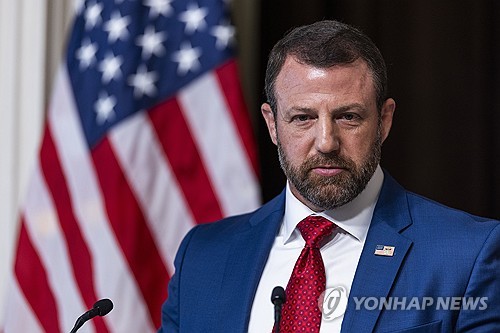
Mark Wayne Mullen, the homeland security secretary, submitted written testimony ahead of a House Homeland Security Committee hearing laying it out plainly. Iranian state actors and Iran-supported operatives have been targeting networks behind American airports, banks, courts, the power grid, hospitals, and water systems.
“Since the Iran war began earlier this year,” Mullen wrote, “Iranian government cyber personnel and pro-Iranian cyber criminals have targeted the United States’ critical infrastructure networks.”
That sentence should sit heavily on every capital allied with Washington. If Tehran can reach into the plumbing of the American heartland, it can reach into the plumbing everywhere else.
The confusing part: not every glitch is a gunshot
Here’s where the story gets deliberately murkier — and why the full picture matters more than any single headline.
Separately, Mullen’s confirmation came just days after a string of high-profile technical outages across major US institutions: Microsoft systems buckled, JP Morgan Chase experienced disruptions, air traffic control grids faltered, and even the National Security Agency’s internal networks showed signs of distress.
That sequence would normally scream attribution. Instead, three separate officials pushed back hard.
Jay Clayton, director of national intelligence, told reporters the outages appeared to stem from “maintenance and technology change-related isolated service disruptions” — not organized attacks. Christopher Ré, the FBI’s deputy director, said the same: no evidence tied recent failures to hostile cyber activity.
So the US government is simultaneously confirming one thing and denying another. Iran is attacking American infrastructure. The recent dramatic outages? Probably nothing to do with it.
That contradiction isn’t accidental. It’s the signature of a conflict being fought in the gray zone — where adversaries want you to suspect everything without giving you enough proof to respond decisively.
Who wins when the battlefield disappears
This is the strategic shift nobody outside intelligence circles is articulating clearly enough.
Traditional deterrence works when the attacker crosses a visible threshold — troops roll across a border, missiles leave silos, ships cross maritime lines. The defender responds because the act is unmistakable.
Cyber attacks against infrastructure don’t land with the same bang. A compromised power grid controller or a sabotaged water treatment sensor doesn’t broadcast who did it, when, or even whether damage was intentional. Malware sits inside a system for months before triggering. Maintenance updates become indistinguishable from sabotage. Outages look like incompetence until proven otherwise.
That ambiguity is exactly what Iran’s playbook exploits — and what China, North Korea, and others are already mastering on their own tracks.
Mullen’s admission signals a shift in US posture: the era of plausible deniability is ending for Tehran, at least in official rhetoric. But the fact that attribution remains contested for the recent wave of outages proves the underlying problem hasn’t changed. The US still struggles to prove, publicly and quickly, who broke in and what they did.
What this means for the Asia-Pacific
Japan, South Korea, Taiwan, Australia, the Philippines — all of them share structural similarities with the United States in this domain.
Their critical infrastructure runs on the same cloud platforms, the same financial clearing systems, the same industrial control software. Their defense ministries rely on the same supply chains. Their regulatory frameworks for incident response move slowly compared to the speed of offensive code.
South Korea deserves particular scrutiny. The country’s financial sector converges tightly — a handful of banking giants process most domestic transactions, and a concentrated network of data centers hosts government and private-sector workloads. Japan’s energy sector depends on aging SCADA systems retrofitted with modern networking, a known vulnerability class. Taiwan’s semiconductor supply chain, while physically defended, passes through digital corridors that cross multiple jurisdictions and ownership structures.
If Iran — a mid-tier military power with limited conventional force projection — can sustain cyber campaigns against US infrastructure for months without triggering a proportional response, the calculus changes dramatically for every US ally in the Indo-Pacific facing far more capable adversaries.
China’s PLAAF Unit 61398 and North Korea’s Reconnaissance General Bureau both possess well-documented capabilities that exceed Iran’s. The question isn’t whether they could target allied infrastructure. The question is whether the US and its partners will recognize the attack before it escalates past recovery.
The harder question: what comes next
Mullen’s testimony opens several doors, some useful, some dangerous.
On the positive side, formal congressional acknowledgment creates political cover for increased funding, clearer interagency mandates, and potentially faster information-sharing protocols with allies. Europe’s NCIG counterparts may find reason to align standards. Japan and South Korea already coordinate cyber defense through trilateral channels — this confirmation strengthens the case for binding joint exercise scenarios that stress-test real-world attack-response chains rather than theoretical ones.
On the risk side, explicit naming raises the stakes. Every subsequent Iranian provocation — even low-level probing scans — carries more political weight. Adversaries may interpret heightened US rhetoric as preparation for kinetic retaliation, which could trigger pre-emptive strikes against perceived vulnerabilities. The line between defensive cyber posturing and offensive escalation is thinner than policymakers admit.
There’s also the domestic credibility trap. If the US continues to announce systemic Iranian cyber threats while simultaneously explaining away major outages as benign maintenance issues, public trust erodes. Businesses lose confidence in shared platform providers. Legislators push for reactive bans rather than durable investment. That pattern repeats itself across every allied democracy watching closely.
The bottom line
Iran’s campaign against US infrastructure proves something uncomfortable: the concept of homeland security in the digital age requires redefinition. Physical borders don’t protect servers. Supply-chain dependencies create vulnerabilities no single nation can eliminate alone.
The Pacific allies understand this intuitively. Islands and peninsulas with concentrated population and economic hubs face proportionally greater exposure than continental states. The question is whether they’re building defenses fast enough — or whether they’ll end up repeating the same attribution struggle the US is living through right now.
The war didn’t start with missiles. It started with someone typing commands into a terminal at 2 AM, waiting for a firewall rule to misfire, and watching a gate open.