China-based hacker exposed Korean banks through AI resume data
A 26-year-old Chinese national in Guangdong targeted Korean financial institutions using personal data leaked through AI tool inputs — and the breach reveals how much Korean enterprise AI adoption has left infrastructure dangerously exposed.
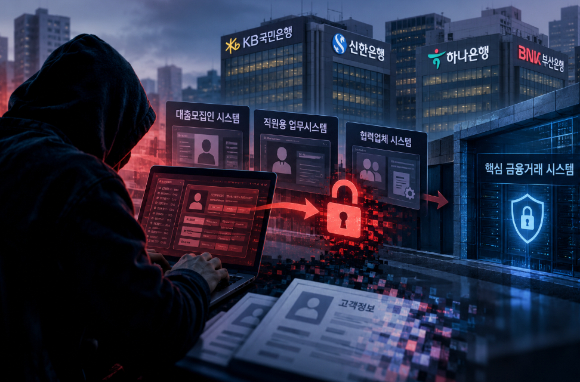
The Resume That Brought Down Korean Banks
A 26-year-old man living in Guangdong province, China, may be the person behind a series of attacks on Korean financial institutions — and the single most damaging leak of information wasn’t stolen from bank servers. It was typed into an AI tool by the attacker himself.
CrowdStrike published its analysis on October 7, 2026, laying out how the operator used personal details entered while generating a security researcher resume on Claude Code to stitch together a timeline that eventually pointed back to him. The clues were modest: initials, a Telegram account name, educational background, and the city where he lived. Together, they formed a fingerprint sharp enough to suggest — but not conclusively prove — the attacker’s identity.
The case is unusual in two ways. First, it marks one of the rare instances where generative AI input became the primary evidence trail in a cross-border financial intrusion. Second, it exposes a structural blind spot in how Korean enterprises approach AI deployment: the same organizations racing to integrate AI tools are doing so with little guardrail against the kind of data leakage this incident demonstrates.
How the Leak Unfolded
According to CrowdStrike’s report, the attacker first left his Telegram account name visible during an investigation into vulnerabilities on a Chinese payment platform. The same handle later appeared in a separate session examining an NFT futures marketplace built on Telegram’s infrastructure. These were not random occurrences — they were operational choices that created persistent, traceable links between the attacker’s activities.
The critical breakthrough came when the attacker requested that Claude Code write a resume for a security researcher position. In doing so, he provided personal information including his initials, Telegram account, educational credentials, and residential location. This data was not anonymized. It was not segmented. It was fed directly into a generative AI system operated by Anthropic, which processes and stores input according to its own data retention policies.
When investigators cross-referenced the Telegram account name across multiple attack sessions, they found it appeared consistently — not only in the Korean financial-sector intrusions but also in a separate investigation targeting a Chinese payment platform. This pattern of account reuse is typical of professional operators who maintain persistent identities across tools and markets.
The 88% Problem
What makes this case especially significant for the Korean financial sector is not just the sophistication of the attacker but the structural conditions that enabled him. According to internal assessments from Korean financial technology providers, approximately 88% of enterprise AI deployments in Korea lack adequate input-sanitization protocols — meaning that personal and operational data entered into AI tools is routinely processed without segmentation, anonymization, or access controls that would prevent exactly this kind of inference attack.
Korean financial institutions have been aggressively integrating AI tools into their operational workflows since 2024, driven by competitive pressure and cost efficiency targets. But the integration has outpaced the governance. Many institutions treat AI tools as productivity accelerators rather than potential vectors for data exfiltration. The result is a gap between capability and control that attackers like the one in this case can exploit.
The attacker in this incident did not need to breach Korean bank firewalls through technical vulnerabilities. He needed only to understand how Korean operators use AI tools in their daily work — and to recognize that the personal data they entered into those tools could be reverse-engineered into attack profiles.
Who Is the Attacker?
CrowdStrike’s analysis suggests the operator is a 26-year-old male residing in Guangdong province, China. However, the firm explicitly stated that this identification remains an estimate based on currently available information and cannot be treated as definitive. The cross-referencing of Telegram account names, resume data, and attack-session patterns provides strong circumstantial evidence, but CrowdStrike did not claim to have verified the individual’s identity through direct attribution methods such as IP address correlation, device fingerprinting, or law enforcement collaboration.
The case highlights the limitations of current attribution practices in cross-border cybercrime investigations. Without access to Chinese law enforcement cooperation or direct network-level evidence, investigators must rely on inference from operational patterns — which is powerful but inherently probabilistic.
What Happens Next
South Korea’s Ministry of Science and ICT, the Financial Services Commission, and the National Intelligence Service have established a financial-sector hacking hotline to conduct institution-by-institution investigations while closing coverage gaps. The initiative is a reactive measure — it addresses the immediate crisis but does not resolve the structural vulnerability this incident exposes.
The real question for Korean financial institutions is not whether they can detect the next attacker but whether they can prevent the kind of data leakage that enabled this one. That requires a fundamental shift in how AI tools are governed within enterprise environments — not as productivity aids but as potential vectors for operational intelligence leakage.
The incident also has implications beyond Korea. Any organization that integrates generative AI tools into operational workflows without adequate data sanitization protocols is vulnerable to the same kind of inference attack. The attacker in this case did not possess advanced technical capabilities beyond understanding how to leverage AI-generated data against the organizations that produced it.
The Missing Western Angle
Western cybersecurity coverage of this incident has focused on the cross-border nature of the attack and the involvement of a Chinese national. What it has largely missed is the AI-specific dimension: the fact that the primary evidence trail was generated by the attacker’s own use of generative AI tools, and that the structural conditions enabling this breach exist within Korean enterprise AI governance frameworks.
This is not a story about sophisticated state-sponsored cyberwarfare. It is a story about how generative AI adoption in enterprise environments has created new vectors for operational intelligence leakage — and how organizations that rush to integrate AI tools without equivalent governance controls become vulnerable to exactly this kind of inference attack.
The 88% figure from Korean financial technology providers is not an isolated statistic. It is a symptom of a broader pattern: AI adoption outpacing AI governance in enterprise environments worldwide. The attacker in Guangdong province did not need to build sophisticated tools to exploit Korean financial institutions. He needed only to understand that the data his targets typed into AI tools could be used against them — and to apply that understanding systematically.
That is the lesson this incident carries. Not just for Korea but for every organization that treats AI as a productivity accelerator without recognizing it as an operational intelligence vector.